
End-to-end automation and load testing need stable ways to create identities, complete verification and repeat scenarios. Reusing production accounts makes tests fragile and risky; leaving test accounts indefinitely can create forgotten access in the real environment.
Make the test identity class explicit
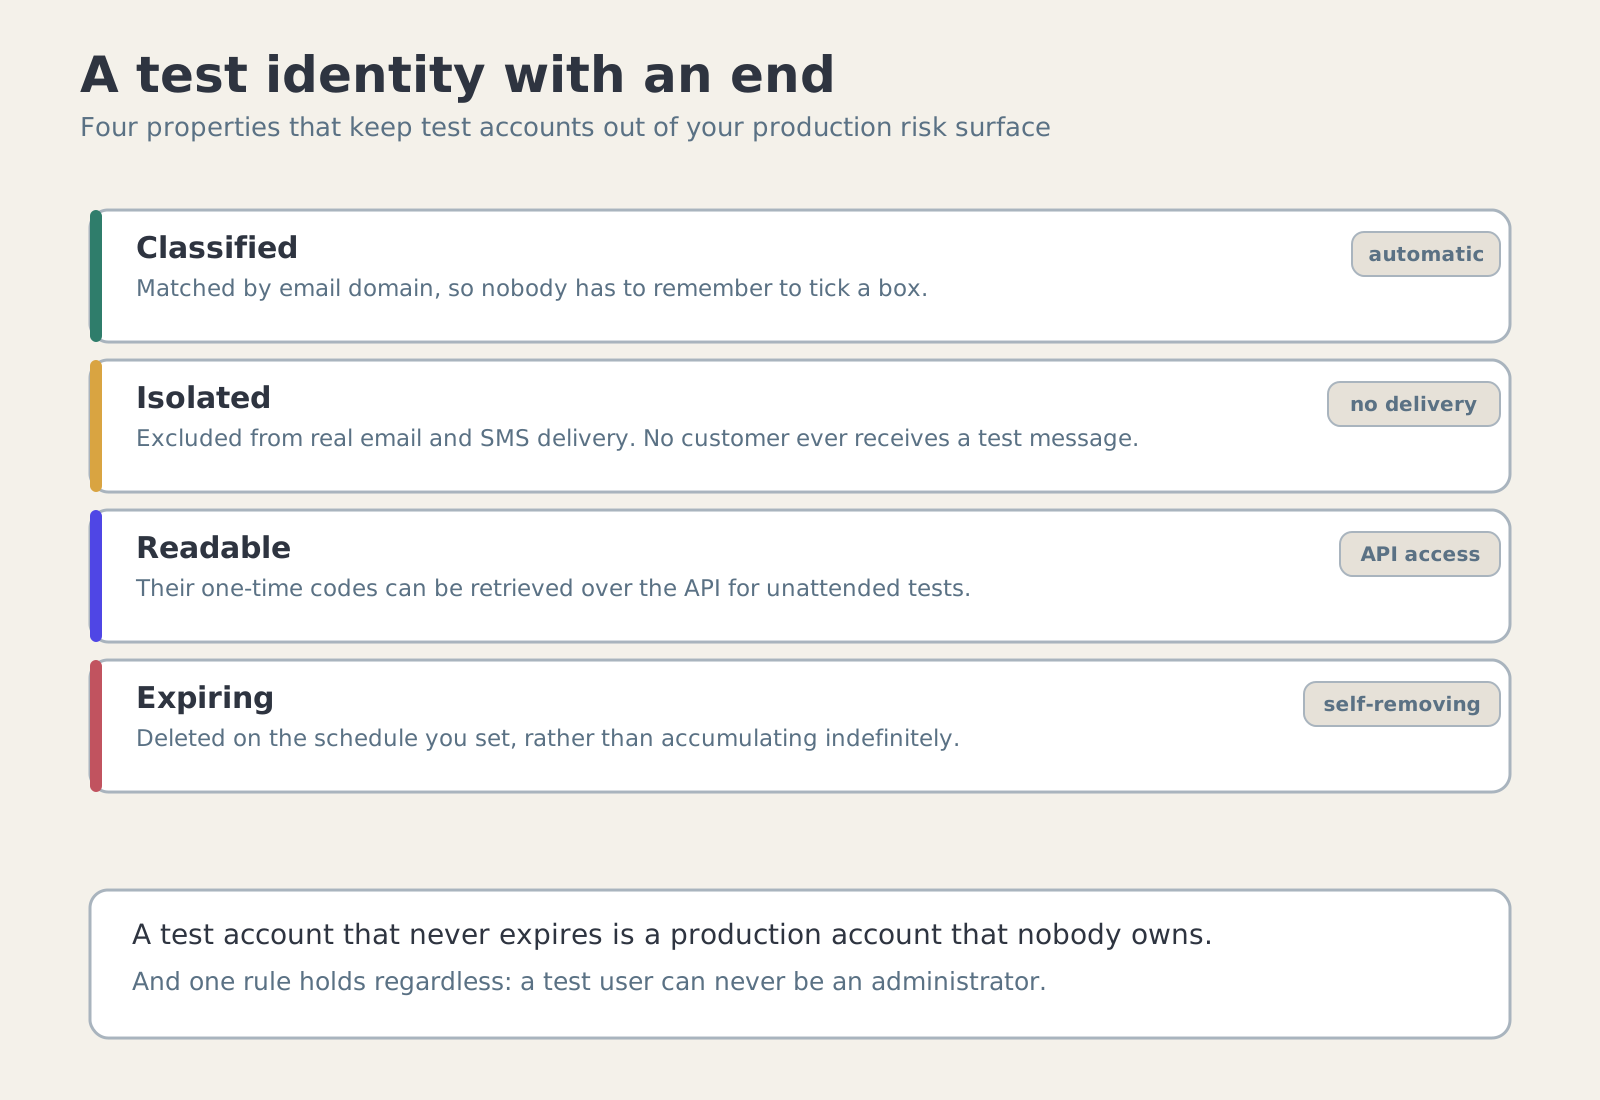
A test identity should be distinguishable by documented rules, not merely a name that begins with “test”. Define which environments and email domains are permitted, which features are enabled and how long an account may exist. The flag must not be user-controlled in a way that bypasses normal safeguards.
WebFrolic’s notes state that test users are disabled by default, can be enabled through lifecycle settings, can have configurable deletion timing and may be identified using configured email domains. They also state that test users cannot be placed in the administrator segment.
Design verification for automation
Automated tests may need to retrieve an OTP without waiting for real email or SMS delivery. A test-specific administrative API can provide that capability, but it must be restricted to authorised test identities and environments. It should never become a general recovery or OTP lookup endpoint for normal accounts.
Keep the OTP scoped to its identity and transaction, and retain the usual expiry and one-time-use expectations. Convenience must not permit a code issued for one user to authenticate another or be replayed indefinitely.
Keep test identities out of privileged segments
The account that can query test verification data should not also be able to grant itself administrator access. Separate permissions to create tests, inspect test OTPs, operate environments and manage privileged user segments. That limits the consequences of a compromised test runner or leaked test credential.
Do not use test accounts as durable infrastructure identities. Workloads that need persistent resource access should use a service or machine identity with a defined purpose rather than extending a test user beyond its lifecycle.
Prove cleanup and isolation
Test that expired test users are removed and can no longer sign in or use credentials. Verify how sessions, memberships and assigned permissions are handled. Watch test-domain classification so a configuration mistake cannot accidentally turn a real person into a test identity.
Keep test data separate from production and avoid sending real customer communications from test workflows. Review lifecycle settings when a CI environment or domain changes, and make the owner of each test environment explicit.
Put it into practice
Close the loop
- Keep test-user enablement off by default and scope it deliberately.
- Set a lifecycle and deletion policy for test identities.
- Restrict OTP lookup to authorised test identities and environments.
- Prohibit test users from administrator segments and verify cleanup.