New
New to identity
Building from scratch, or choosing your first provider? See what the platform covers, then try it free.
See the platform ↗Identity · Access · Support
One provider for your customers, your workforce and your AI agents, authentication, authorization, the help desk and the IT service desk in one place, under separate rules that never mix. Built from the lessons of real identity breaches.
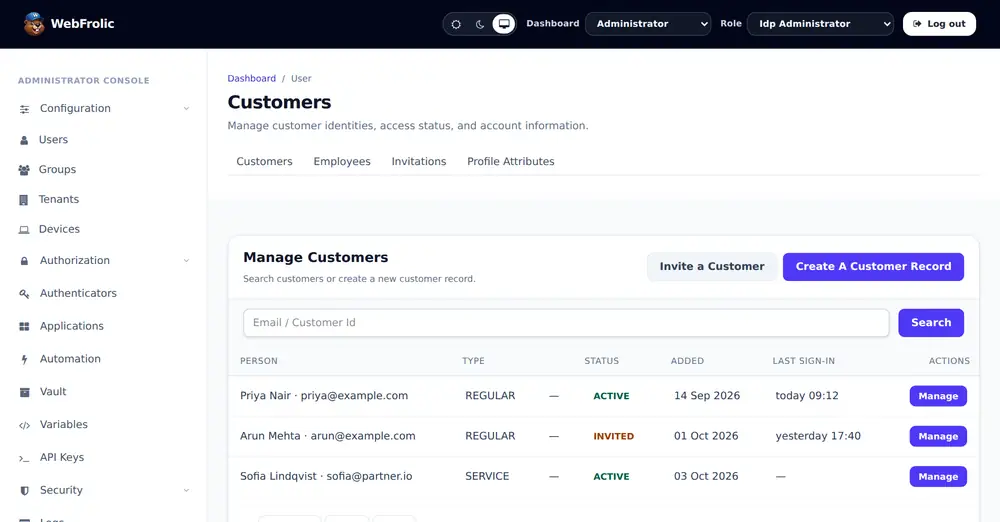
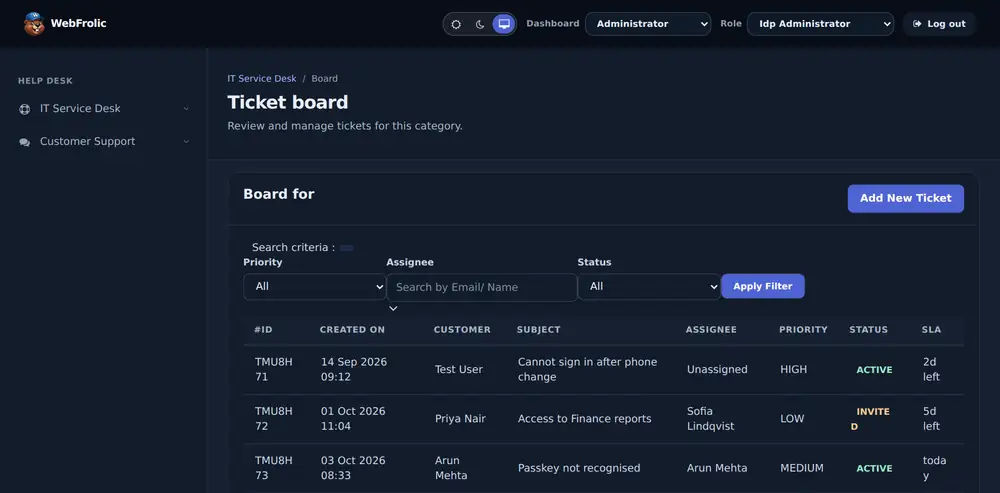
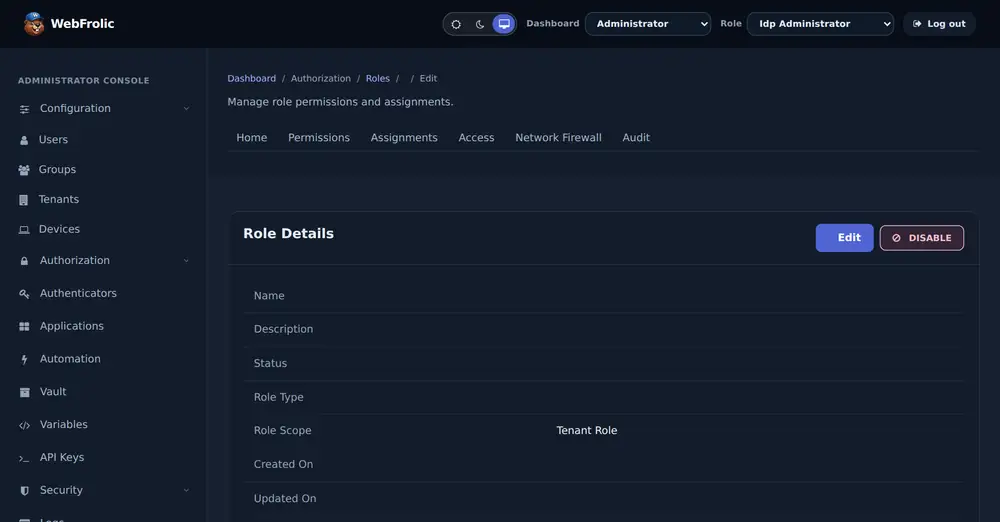
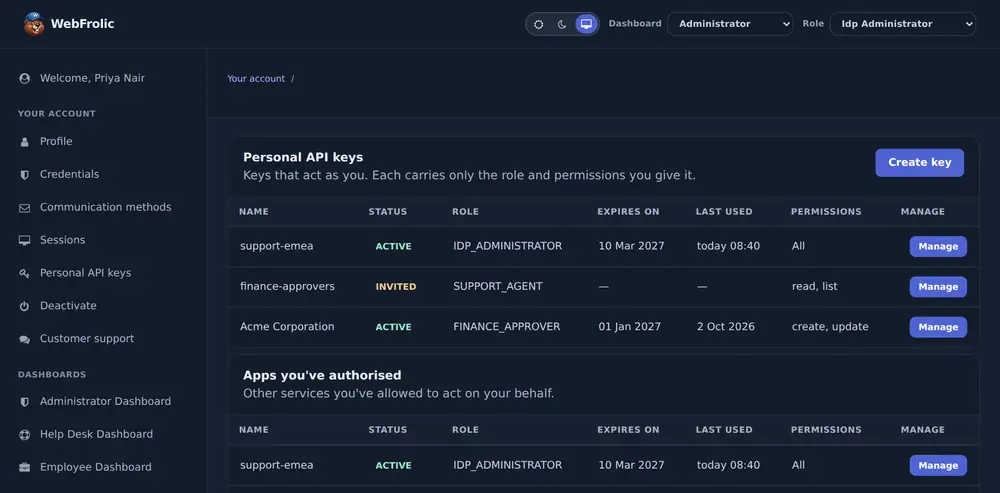
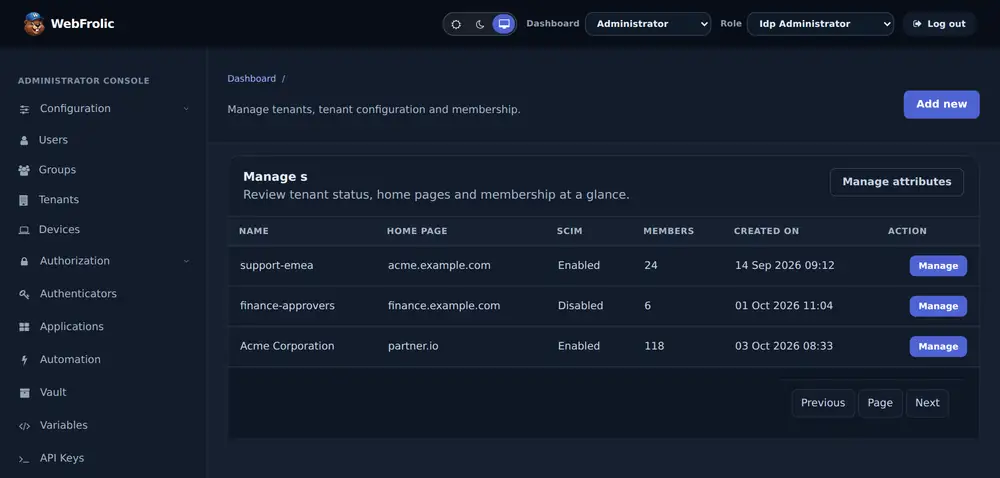
The WebFrolic administrator console. Explore it in the live demo ↗
For startups
Startups need enterprise-grade identity from day one, without hiring a team to run it. We partner differently: the full WebFrolic platform, free for your first year, in exchange for a 2% equity stake, so we grow only when you do. Hands-on help is billed by the hour, never locked in.
Find your path
Tell us where you are, and we’ll point you to the part of WebFrolic that helps most.
New
Building from scratch, or choosing your first provider? See what the platform covers, then try it free.
See the platform ↗Switching
Have a provider, but it’s missing things? See how WebFrolic compares and the capabilities others skip: MCP, cross-app access, token binding, verifiable credentials.
See what’s different ↗Switching
Have a provider, but it’s too expensive? See transparent usage pricing, a free tier, and the startup equity model.
See pricing ↗The problem
Every sign-in, token and permission runs through identity. Build it yourself and a subtle mistake becomes a breach; buy enterprise identity and you pay for complexity you don’t need and a team to run it. Most teams, early ones most of all, have neither the time nor the specialists to get it right.
Critical path
Every sign-in, token and permission depends on identity. When it is wrong or down, so is your product.
Easy to get wrong
Session handling, token storage, recovery flows, the subtle parts are exactly where incidents start.
No team for it
Identity expertise is scarce and expensive. Few teams can dedicate someone to getting it right.
WebFrolic is one platform for every kind of identity, customers, workforce and agents, with separate rules that never mix, so you won’t outgrow it or stitch tools together later. Read the identity-house essay →
What WebFrolic does
Start with the area you need today; the rest is already there when you need it. Prefer another view? Browse by product, by solution or take the interactive product tour.
Customer identity
Workforce identity
AI agents
Access & governance
Operations
Everything else
Pricing
Usage-based pricing, per unit per month, with no forced bundles.
Customer identity
per monthly active customer after the first 25,000, every month.
Estimate your cost ↗Workforce identity
per workforce user per month, with SSO, MFA, lifecycle, access governance and the IT service desk available.
Estimate your cost ↗Startups and non-profits
for eligible startups through the equity-backed startup partnership; 50% off for non-profits and education.
See the programs ↗Built from breach lessons
We studied how well-known identity incidents actually happened. Most began at an everyday seam, not a dramatic exploit.
| Where it goes wrong | The usual approach | WebFrolic |
|---|---|---|
| The support desk | Agents hold standing access to every customer record in a separate tool. | Support is built in. Agents see a customer only with an open ticket assigned to them, and impersonate only where the category allows. How it works |
| Access requests | A ticket in one system, a manual change in another, and senior requests that skip approval. | Approved requests execute themselves; manual changes need a valid service ticket ID; the same workflow applies whoever asks. How it works |
| AI agents and integrations | A shared service account or a person’s API key, with every permission they have. | Agents get their own identity and short-lived tokens; secrets stay in the vault; you choose per operation what an API key may call. MCP clients come only from a catalog you approve, and tokens can be bound to the client with DPoP. How it works |
| Multi-factor authentication | “Two methods” counted as two factors, even when both can be phished. | Session assurance is calculated from each method’s characteristics, factor type, phishing resistance, device binding. How it works |
| Privileged access | Standing admin rights and shared admin logins. | Privileged roles need step-up and approved networks, grants expire, and shared jobs run as service users. How it works |
| Account recovery | The ordinary password-reset path, open to whoever can answer a question. | Recovery is its own ceremony with its own methods and assurance, and support issues recovery codes instead of resetting credentials. How it works |
Read the security white paper: Only as Secure as the Weakest Link →
Identity debt
Orphaned service accounts, stale test users, permissions no one revisits, keys that never rotate, all-or-nothing delegation, privileges buried in groups, the access that accumulates is the access that gets exploited. WebFrolic is built so it can’t.
See the product
Six dashboards share one sign-in: Customer, Employee, Administrator, Customer Support, IT Service Desk and Tenant Administrator.
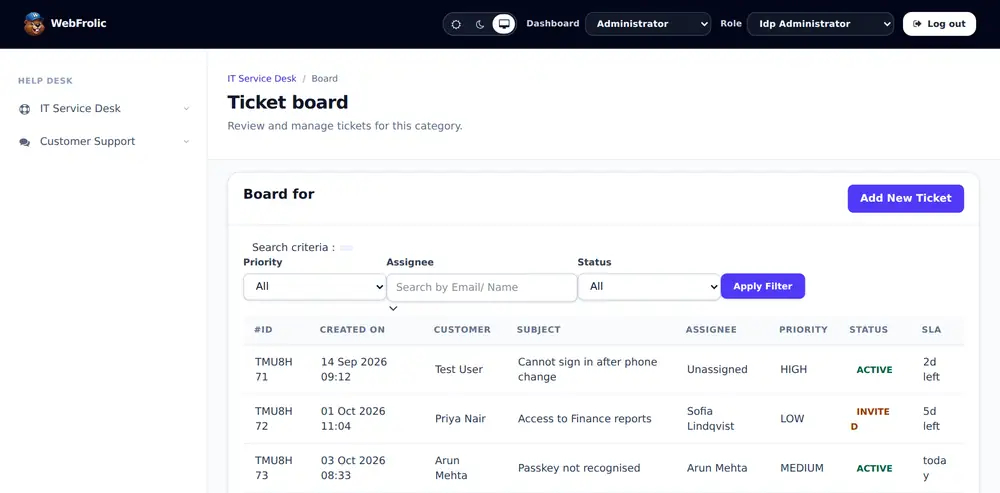
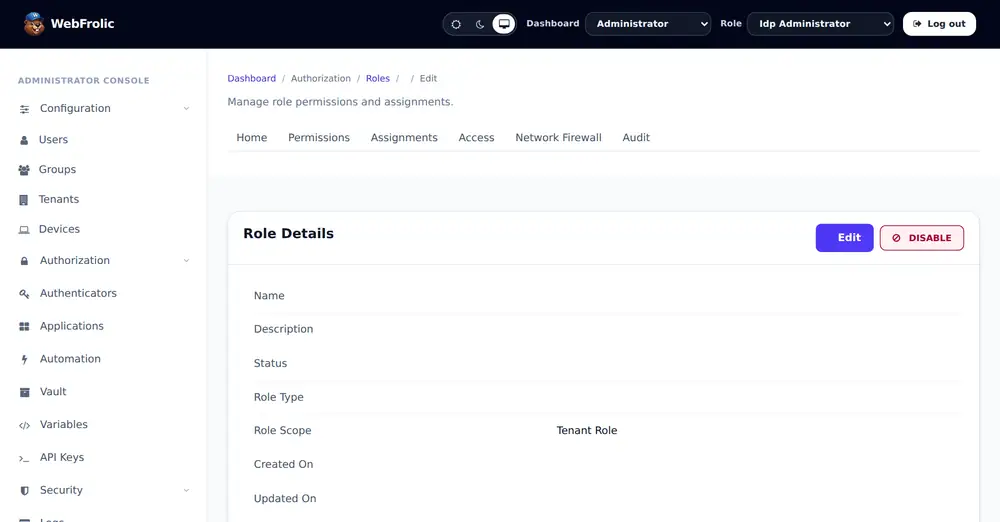
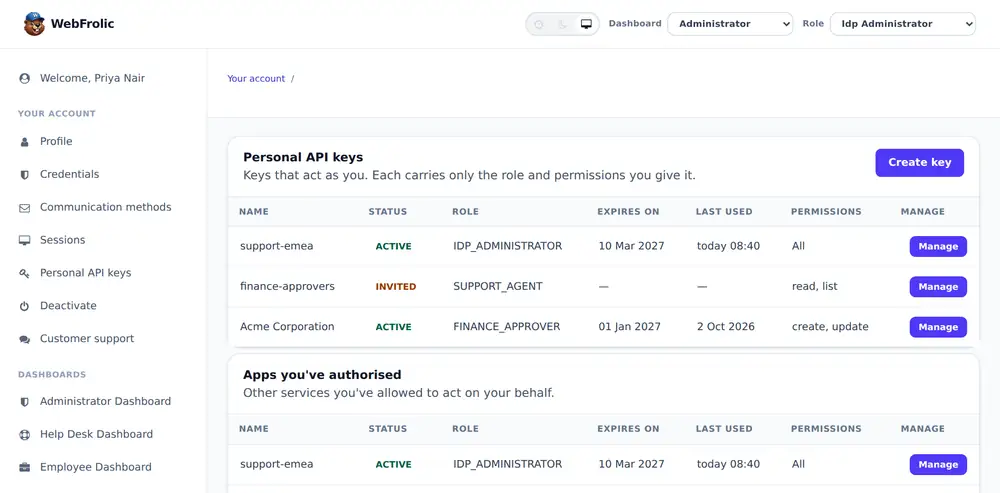
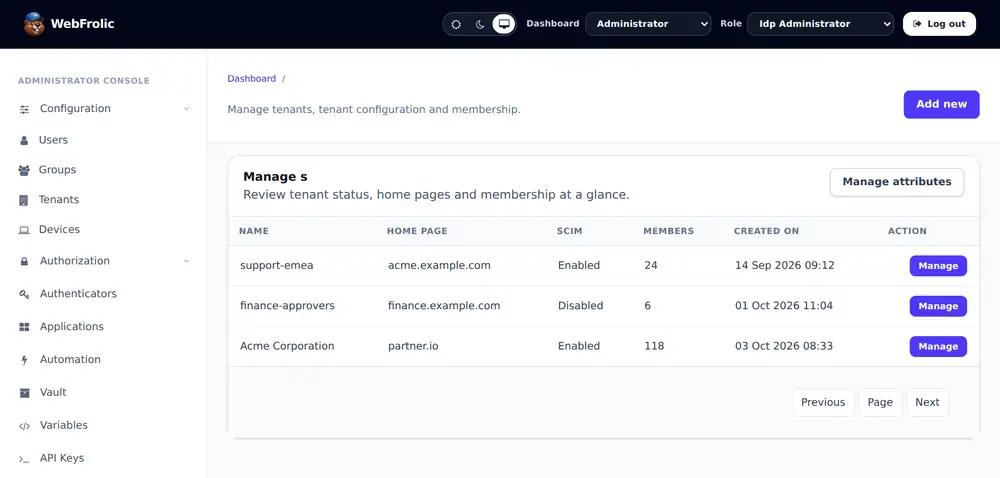
Try it yourself. Explore the dashboards and features on the live demo, no sign-up required.
Open demo.webfrolic.comSee the model at work
Pick a situation to see which identities, controls and records are involved.
Scenario 01
A support agent built on an LLM needs to create a calendar event in the customer’s own third-party account. It should use the customer’s consent, not a shared admin key, and never hold the customer’s refresh token.
Scenario 02
A customer joins the company as an employee. Their identity has to move to the employee persona, with workforce rules, rather than leaving elevated access on a customer account.
Scenario 03
A B2B customer wants to manage its own members and connect its own identity provider, while you keep control of platform-wide policy.
Scenario 04
Recovery is where many account takeovers happen. WebFrolic treats it as its own ceremony and limits what support staff can do.
Depth you can check
Check our work
We don’t publish invented customer logos or certifications we do not hold. Here is what you can inspect for yourself, and developers can start from the developer overview, the build checklist or the community.
Live demo
Explore the product on demo.webfrolic.com without signing up.
Design
The security white paper by founder Sandeep Dhankar explains the breach patterns behind each design decision.
Fit
The comparison matrix shows where WebFrolic stands out and where a specialist may fit better, with sources.
Common questions
An identity provider for your customers, your workforce and your AI agents. It covers sign-up and sign-in, single sign-on, provisioning, authorization, privileged access, access requests and reviews, customer support and IT service desks, and audit, with separate rules for customers, employees and administrators.
Yes. The live demo at demo.webfrolic.com lets you explore the dashboards and features without creating an account.
Yes. Agents run as service or machine users, get scoped access tokens from OAuth2 secrets in the vault, and can act for a consenting user through Connections. Client secrets and refresh tokens never leave the identity provider. For your own APIs, the custom authorization server lets you choose, operation by operation, what agents may call with an API key.
Yes. Many teams get more from improving what they already run than from a migration. Our advisory services work like a fiduciary adviser for identity security: in your interest, with no commissions or referral fees from the products we recommend, aiming to lower costs and improve your security posture. Our ecosystem advisory and onsite support maps your current setup and helps you make changes in place, assessment and evaluation helps you name the problem and weigh the options, and an identity team on retainer gives you part-time experts who review changes to your identity and security flows. All three are available whether or not you use WebFrolic.
OpenID Connect and OAuth 2.1 (PKCE is required for authorization-code flows), SAML 2.0, SCIM 2.0 and WebAuthn/FIDO2. Applications can use six types, and people can sign in with eleven methods, including passkeys and security keys.
You pay for what you use, per unit per month. The first 25,000 monthly active customers are free, workforce users are $2 each, and early-stage startups can use WebFrolic for their first year with no cash through the startup partnership. Model your own estimate in the pricing calculator.
The authorization server for your own APIs is available as open-source binaries you can run yourself, or hosted by WebFrolic. Talk to us about deployment options for the identity provider.
Read the security white paper, try the demo, then ask us to walk through the exact policy and recovery paths you need. We do not publish invented customer results or certifications we do not hold.
Get started
Explore the live demo without signing up, estimate your cost in a minute, or book a walkthrough of the policy, integration and recovery paths you need.